 Phalanx
Own product
Full obligation
You are the manufacturer. The deadlines run for you, and the platform prepares the export for the single reporting platform.
Cyber Resilience Act
Regulation (EU) 2024/2847 requires manufacturers of products with digital elements to report actively exploited vulnerabilities and severe incidents. The first question is not how you report. It is whether you must. The CRA package can be used on its own for products, SBOMs and reporting. It includes access to the vulnerability register. Cases and monitoring are not included in this package.
11 September 2026The date the reporting obligations took effect.
Step one
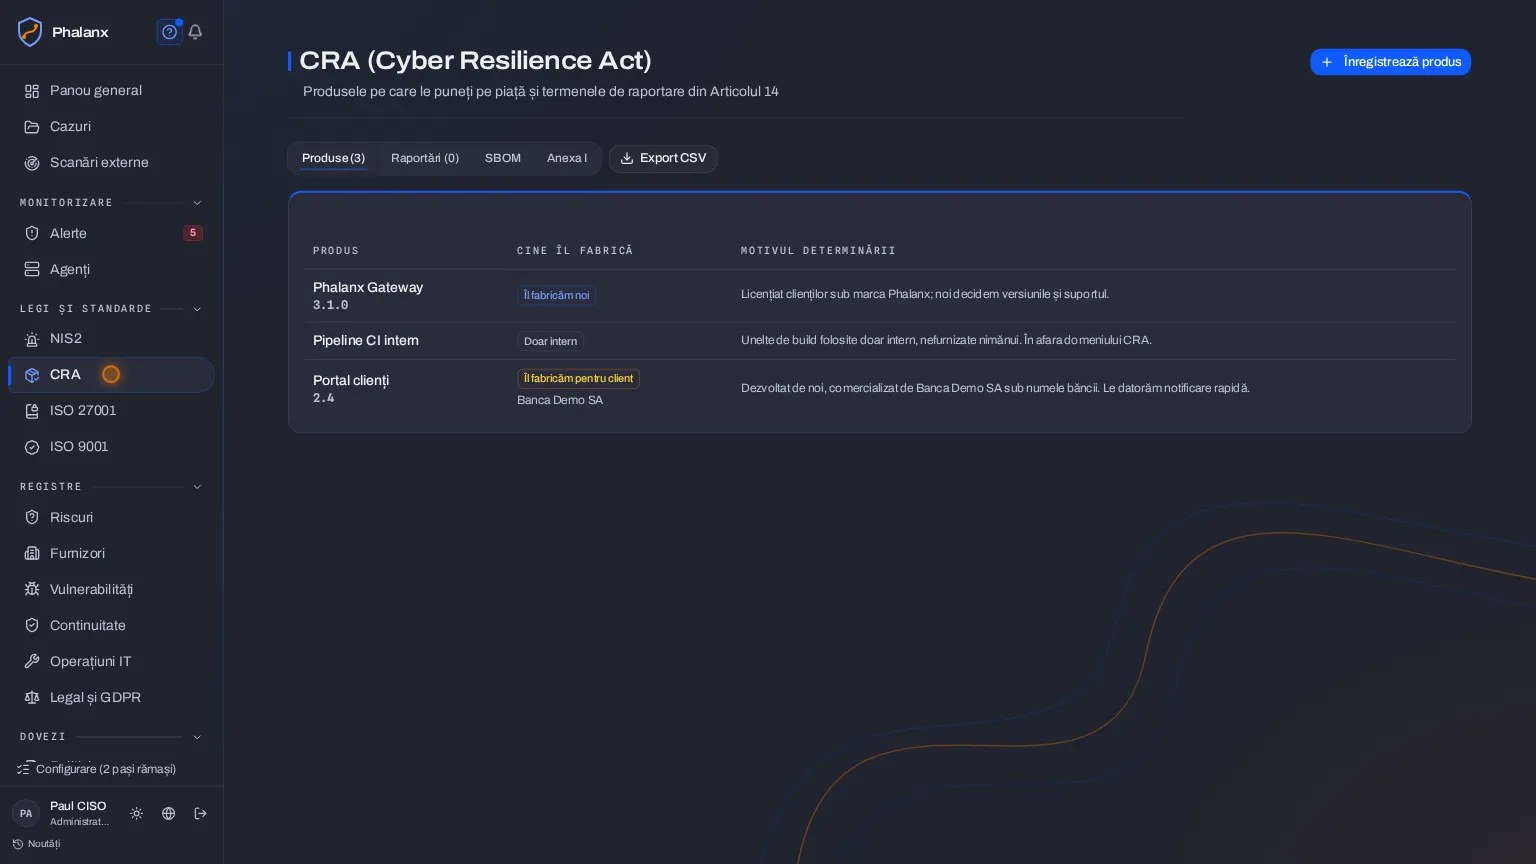
Scope determination is not setup you do before the feature works. It is the feature first deliverable, and it is what stops the platform from opening a regulatory clock on a company with no standing to file anything. Every product gets a role, and the role decides what you owe.
Full obligation
You are the manufacturer. The deadlines run for you, and the platform prepares the export for the single reporting platform.
Contractual notice, no filing
Somebody else is the manufacturer. What you owe is fast notice to them, on a contractual clock, because their 24 hours starts when they become aware and your silence spends it. The platform produces no filing export for this role.
Out of scope
Not covered by the regulation. Recorded anyway, because a dated negative determination is exactly what an auditor wants when they ask why you filed nothing.
The deadlines
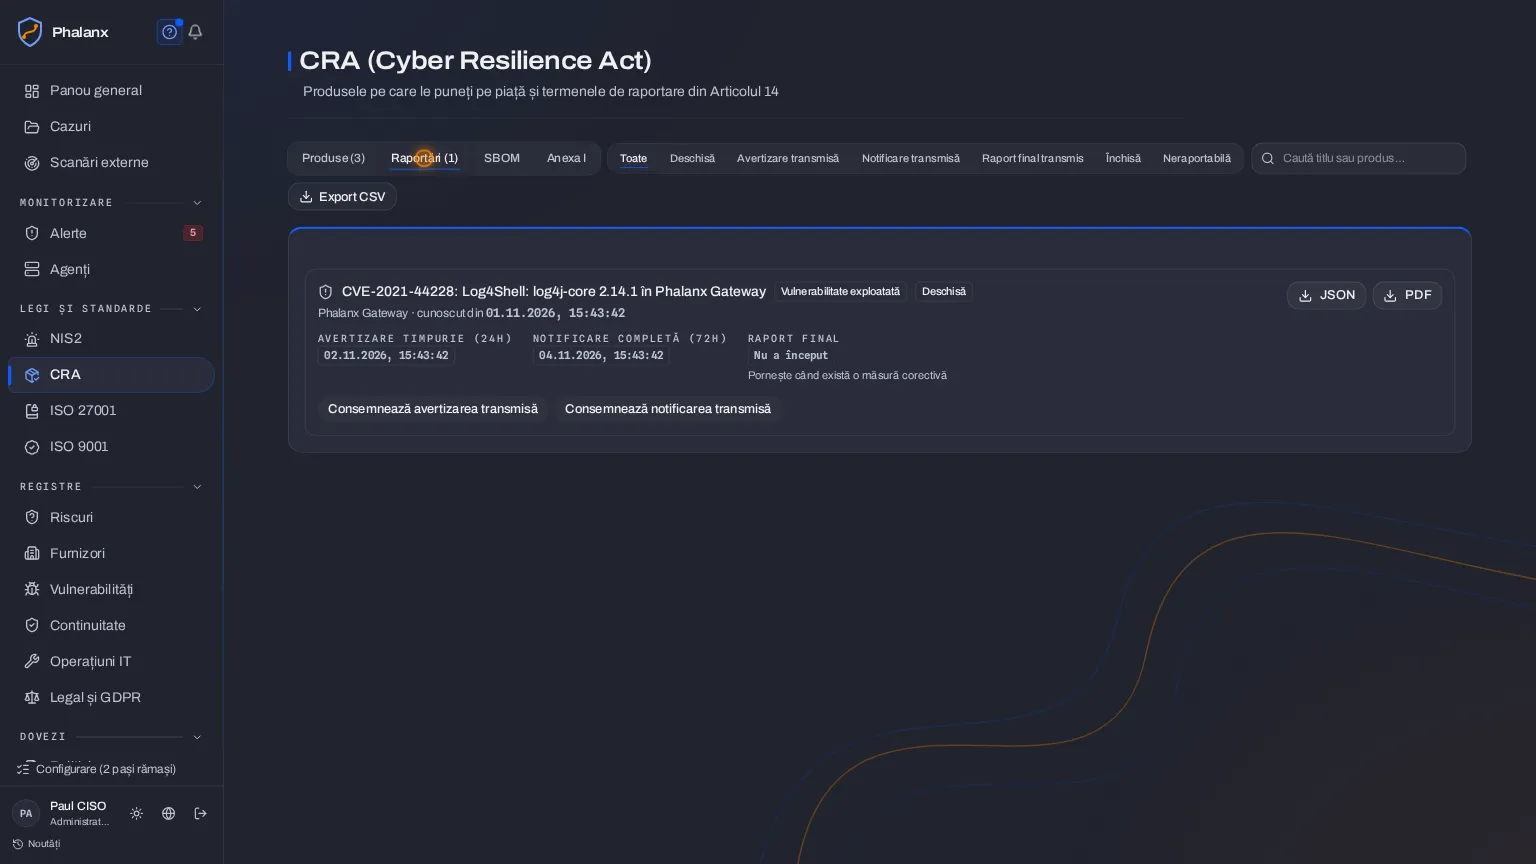
The 24 and 72 hour deadlines start at awareness. The final vulnerability report starts from availability of a corrective measure; the final incident report starts from the full notification.
24 h
Early warning
The first notification, from the moment you became aware.
72 h
Full notification
The complete description of the vulnerability or incident and the measures taken.
14 days
Final report, vulnerability
From the point a corrective measure is available.
1 month
Final report, incident
From the 72 hour full notification.
What else the module does
SBOM
Upload the component list and link vulnerabilities to the product. Matching does not open a CRA report automatically. A person determines whether a vulnerability is actively exploited and records when they became aware.
Annex I
The essential cybersecurity requirements overlay your active ISO 27001 controls, the same way NIS2 does. No second document set for a second regulation.
Register
What was sent, when, to whom, and off which finding. Missed deadlines are flagged as missed rather than quietly absorbed.
Export
The content the single reporting platform asks for, prepared for the CSIRT in the state where you are established. For Romania, that is DNSC.
The boundary
Submission to the ENISA single reporting platform stays an act of your company, performed by a person who answers for it. We say so here because this is the kind of claim a buyer checks during the security review, and an ambiguous phrasing costs more than a missing page.